CHAPTER 06 · SAFETY & SECURITY OPERATIONS

CHAPTER 06 · SAFETY & SECURITY OPERATIONS

06

06

06

Keeping watch, on camera and in the logs.

Keeping watch, on camera and in the logs.

Keeping watch, on camera and in the logs.

Security has two sides for me. At NVIDIA Taiwan I kept watch over cameras, doors and alarms across several campuses; in training labs I learn the analyst side, hunting through logs with KQL and scanning machines for weak spots.

Security has two sides for me. At NVIDIA Taiwan I kept watch over cameras, doors and alarms across several campuses; in training labs I learn the analyst side, hunting through logs with KQL and scanning machines for weak spots.

Security has two sides for me. At NVIDIA Taiwan I kept watch over cameras, doors and alarms across several campuses; in training labs I learn the analyst side, hunting through logs with KQL and scanning machines for weak spots.

NVIDIA TAIWAN · G4S

NVIDIA TAIWAN · G4S

NOV 2025 – JUL 2026

NOV 2025 – JUL 2026

SECURITY+

SECURITY+

Illustration: hooded figures standing among office desks in dim teal light

ROLE

ROLE

Regional Security Operator

Regional Security Operator

Regional Security Operator

WHERE

WHERE

NVIDIA Taiwan (G4S assignment) · multi-⁠campus

NVIDIA Taiwan (G4S assignment) · multi-⁠campus

NVIDIA Taiwan (G4S assignment) · multi-⁠campus

WHEN

WHEN

Nov 2025 – Jul 2026

Nov 2025 – Jul 2026

Nov 2025 – Jul 2026

TOOLS

TOOLS

Sentinel · Defender for Endpoint · KQL · Tenable · MITRE ATT&CK

Sentinel · Defender for Endpoint · KQL · Tenable · MITRE ATT&CK

Sentinel · Defender for Endpoint · KQL · Tenable · MITRE ATT&CK

IN NUMBERS

IN NUMBERS

2,000+

2,000+

2,000+

CAMERAS & READERS

CAMERAS & READERS

monitored across multi-campus facilities

monitored across multi-campus facilities

4

4

4

CERTIFICATIONS

CERTIFICATIONS

OSHA 30, CompTIA Security+, Google Cybersecurity, Cisco Networking Basics

OSHA 30, CompTIA Security+, Google Cybersecurity, Cisco Networking Basics

30

30

30

OSHA HOURS

OSHA HOURS

General Industry, completed 25 Aug 2026

General Industry, completed 25 Aug 2026

01 / 04 · ON SHIFT

01 / 04 · ON SHIFT

On shift at NVIDIA Taiwan

On shift at NVIDIA Taiwan

On shift at NVIDIA Taiwan

From November 2025 to July 2026 I was a Regional Security Operator at NVIDIA Taiwan, on assignment through G4S. I watched 2,000+ cameras and access-control readers across several campuses, answered fire alarms and evacuations, and wrote up injuries, near-misses and unsafe conditions. When incidents overlapped, I sorted them by potential harm and kept senior staff informed. I learned the site’s own systems from scratch.

From November 2025 to July 2026 I was a Regional Security Operator at NVIDIA Taiwan, on assignment through G4S. I watched 2,000+ cameras and access-control readers across several campuses, answered fire alarms and evacuations, and wrote up injuries, near-misses and unsafe conditions. When incidents overlapped, I sorted them by potential harm and kept senior staff informed. I learned the site’s own systems from scratch.

From November 2025 to July 2026 I was a Regional Security Operator at NVIDIA Taiwan, on assignment through G4S. I watched 2,000+ cameras and access-control readers across several campuses, answered fire alarms and evacuations, and wrote up injuries, near-misses and unsafe conditions. When incidents overlapped, I sorted them by potential harm and kept senior staff informed. I learned the site’s own systems from scratch.

ON SHIFT · NVIDIA TAIWAN (G4S)

2,000+

2,000+

2,000+

cameras & access-control readers

cameras & access-control readers

RESPONDED TO

Fire alarms & evacuations

Fire alarms & evacuations

WROTE UP

Injuries, near-misses, unsafe conditions

Injuries, near-misses, unsafe conditions

TRIAGED

Overlapping live incidents

Overlapping live incidents

LEARNED

Site systems from scratch

Site systems from scratch

OSHA OUTREACH

OSHA 30-Hour General Industry

25 Aug 2026 · 30 credit hours · 3.0 CEUs

VIEW CERTIFICATE ↗

COMPTIA

Security+ (SY0-701)

Aug 2025

GOOGLE · COURSERA

Cybersecurity Professional Certificate

2024

CISCO NETWORKING ACADEMY

Networking Basics

Certificate

CompTIA Security+ certified badge, Plus Series

02 / 04

01 · CompTIA Security+ (SY0-701)

Log(N) Pacific Cyber Range certificate of completion for Peter W Pan, September 1, 2025

02 · Log(N) Pacific Cyber Range, Sept 2025

CompTIA Security+ certified badge, Plus Series

02 / 04

01 · CompTIA Security+ (SY0-701)

Log(N) Pacific Cyber Range certificate of completion for Peter W Pan, September 1, 2025

02 · Log(N) Pacific Cyber Range, Sept 2025

02 / 04 · TRAINING

02 / 04 · TRAINING

Training: Security+ and the cyber range

Training: Security+ and the cyber range

Training: Security+ and the cyber range

Alongside the Google Cybersecurity Professional Certificate (Coursera, 2024) and Cisco’s Networking Basics, I earned CompTIA Security+ (SY0-701) in August 2025. Then I went hands-on. The Log(N) Pacific Cyber Range, a training program I completed in September 2025, gave me Azure virtual machines and their logs to practise on. Everything further down this page is lab work, not work for an employer.

Alongside the Google Cybersecurity Professional Certificate (Coursera, 2024) and Cisco’s Networking Basics, I earned CompTIA Security+ (SY0-701) in August 2025. Then I went hands-on. The Log(N) Pacific Cyber Range, a training program I completed in September 2025, gave me Azure virtual machines and their logs to practise on. Everything further down this page is lab work, not work for an employer.

Alongside the Google Cybersecurity Professional Certificate (Coursera, 2024) and Cisco’s Networking Basics, I earned CompTIA Security+ (SY0-701) in August 2025. Then I went hands-on. The Log(N) Pacific Cyber Range, a training program I completed in September 2025, gave me Azure virtual machines and their logs to practise on. Everything further down this page is lab work, not work for an employer.

03 / 04 · THREAT HUNTING

03 / 04 · THREAT HUNTING

Threat hunting with KQL

Threat hunting with KQL

Threat hunting with KQL

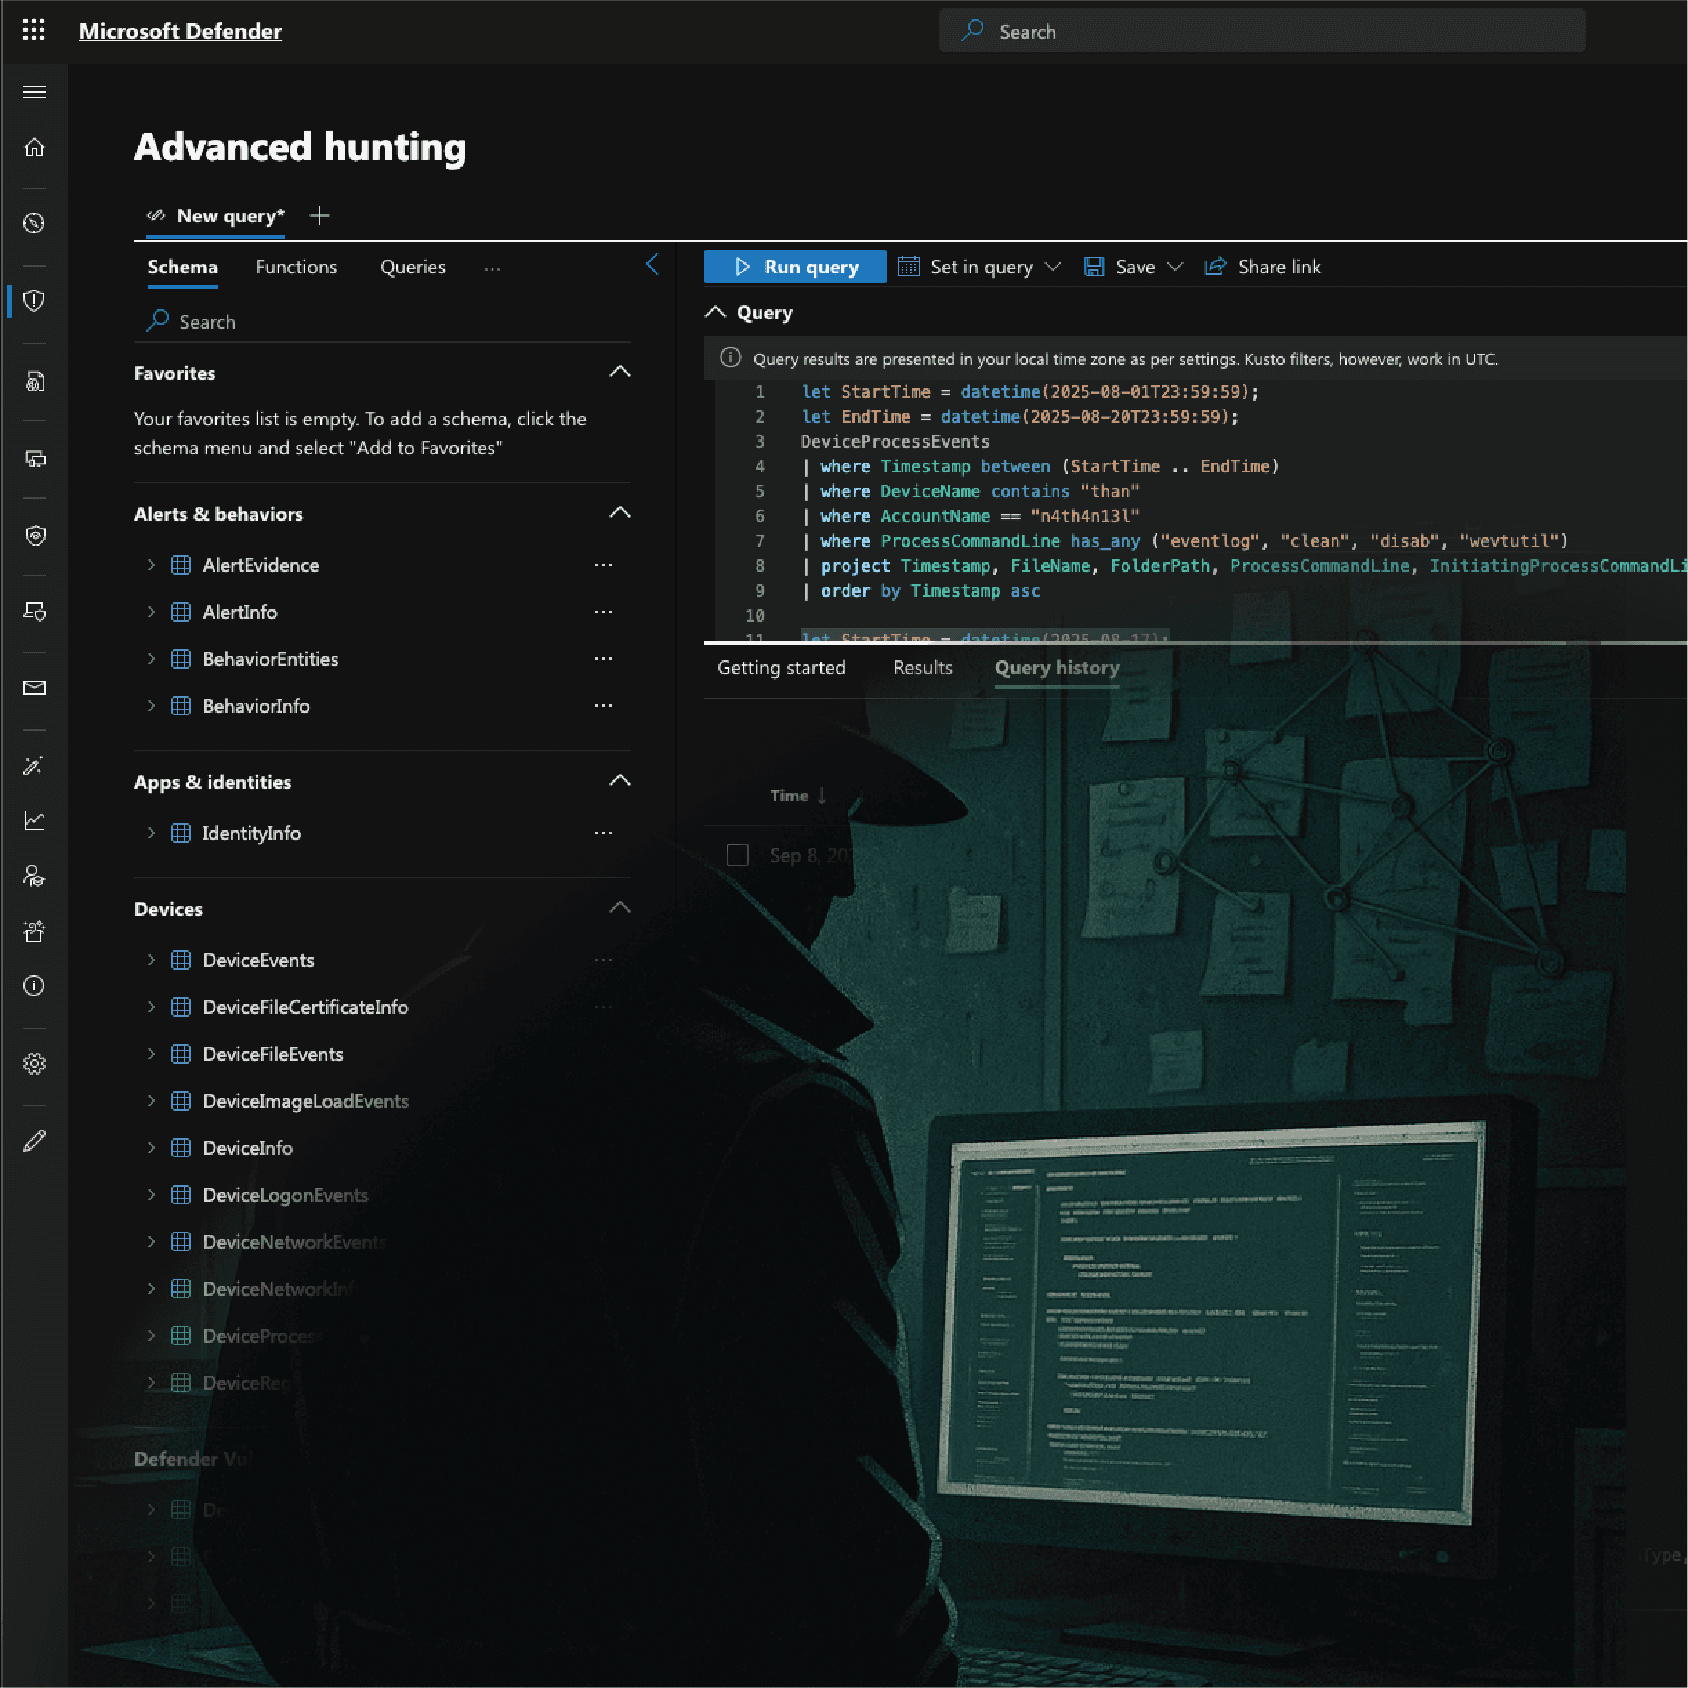
In Microsoft Defender for Endpoint and Microsoft Sentinel I write KQL queries that dig through process, logon and network events for the trail an intruder leaves behind. I map each step to MITRE ATT&CK and write the hunt up from first clue to full attack chain; the write-ups are public on GitHub. I’m also building an Agentic SOC Analyst, a helper that leaves the escalation call to a person.

In Microsoft Defender for Endpoint and Microsoft Sentinel I write KQL queries that dig through process, logon and network events for the trail an intruder leaves behind. I map each step to MITRE ATT&CK and write the hunt up from first clue to full attack chain; the write-ups are public on GitHub. I’m also building an Agentic SOC Analyst, a helper that leaves the escalation call to a person.

In Microsoft Defender for Endpoint and Microsoft Sentinel I write KQL queries that dig through process, logon and network events for the trail an intruder leaves behind. I map each step to MITRE ATT&CK and write the hunt up from first clue to full attack chain; the write-ups are public on GitHub. I’m also building an Agentic SOC Analyst, a helper that leaves the escalation call to a person.

LAB WORK

Threat-hunt write-ups ↗

Threat-hunt write-ups ↗

Microsoft Defender advanced hunting: a KQL query over DeviceProcessEvents

03 / 04

03 · KQL hunt in Microsoft Defender

03 · KQL hunt in Microsoft Defender

ENLARGE

ENLARGE

“

“

“

FROM PART 04 · WEAK SPOTS

FROM PART 04 · WEAK SPOTS

Hunting shows what already happened; scanning shows what could happen next.

Hunting shows what already happened; scanning shows what could happen next.

Hunting shows what already happened; scanning shows what could happen next.

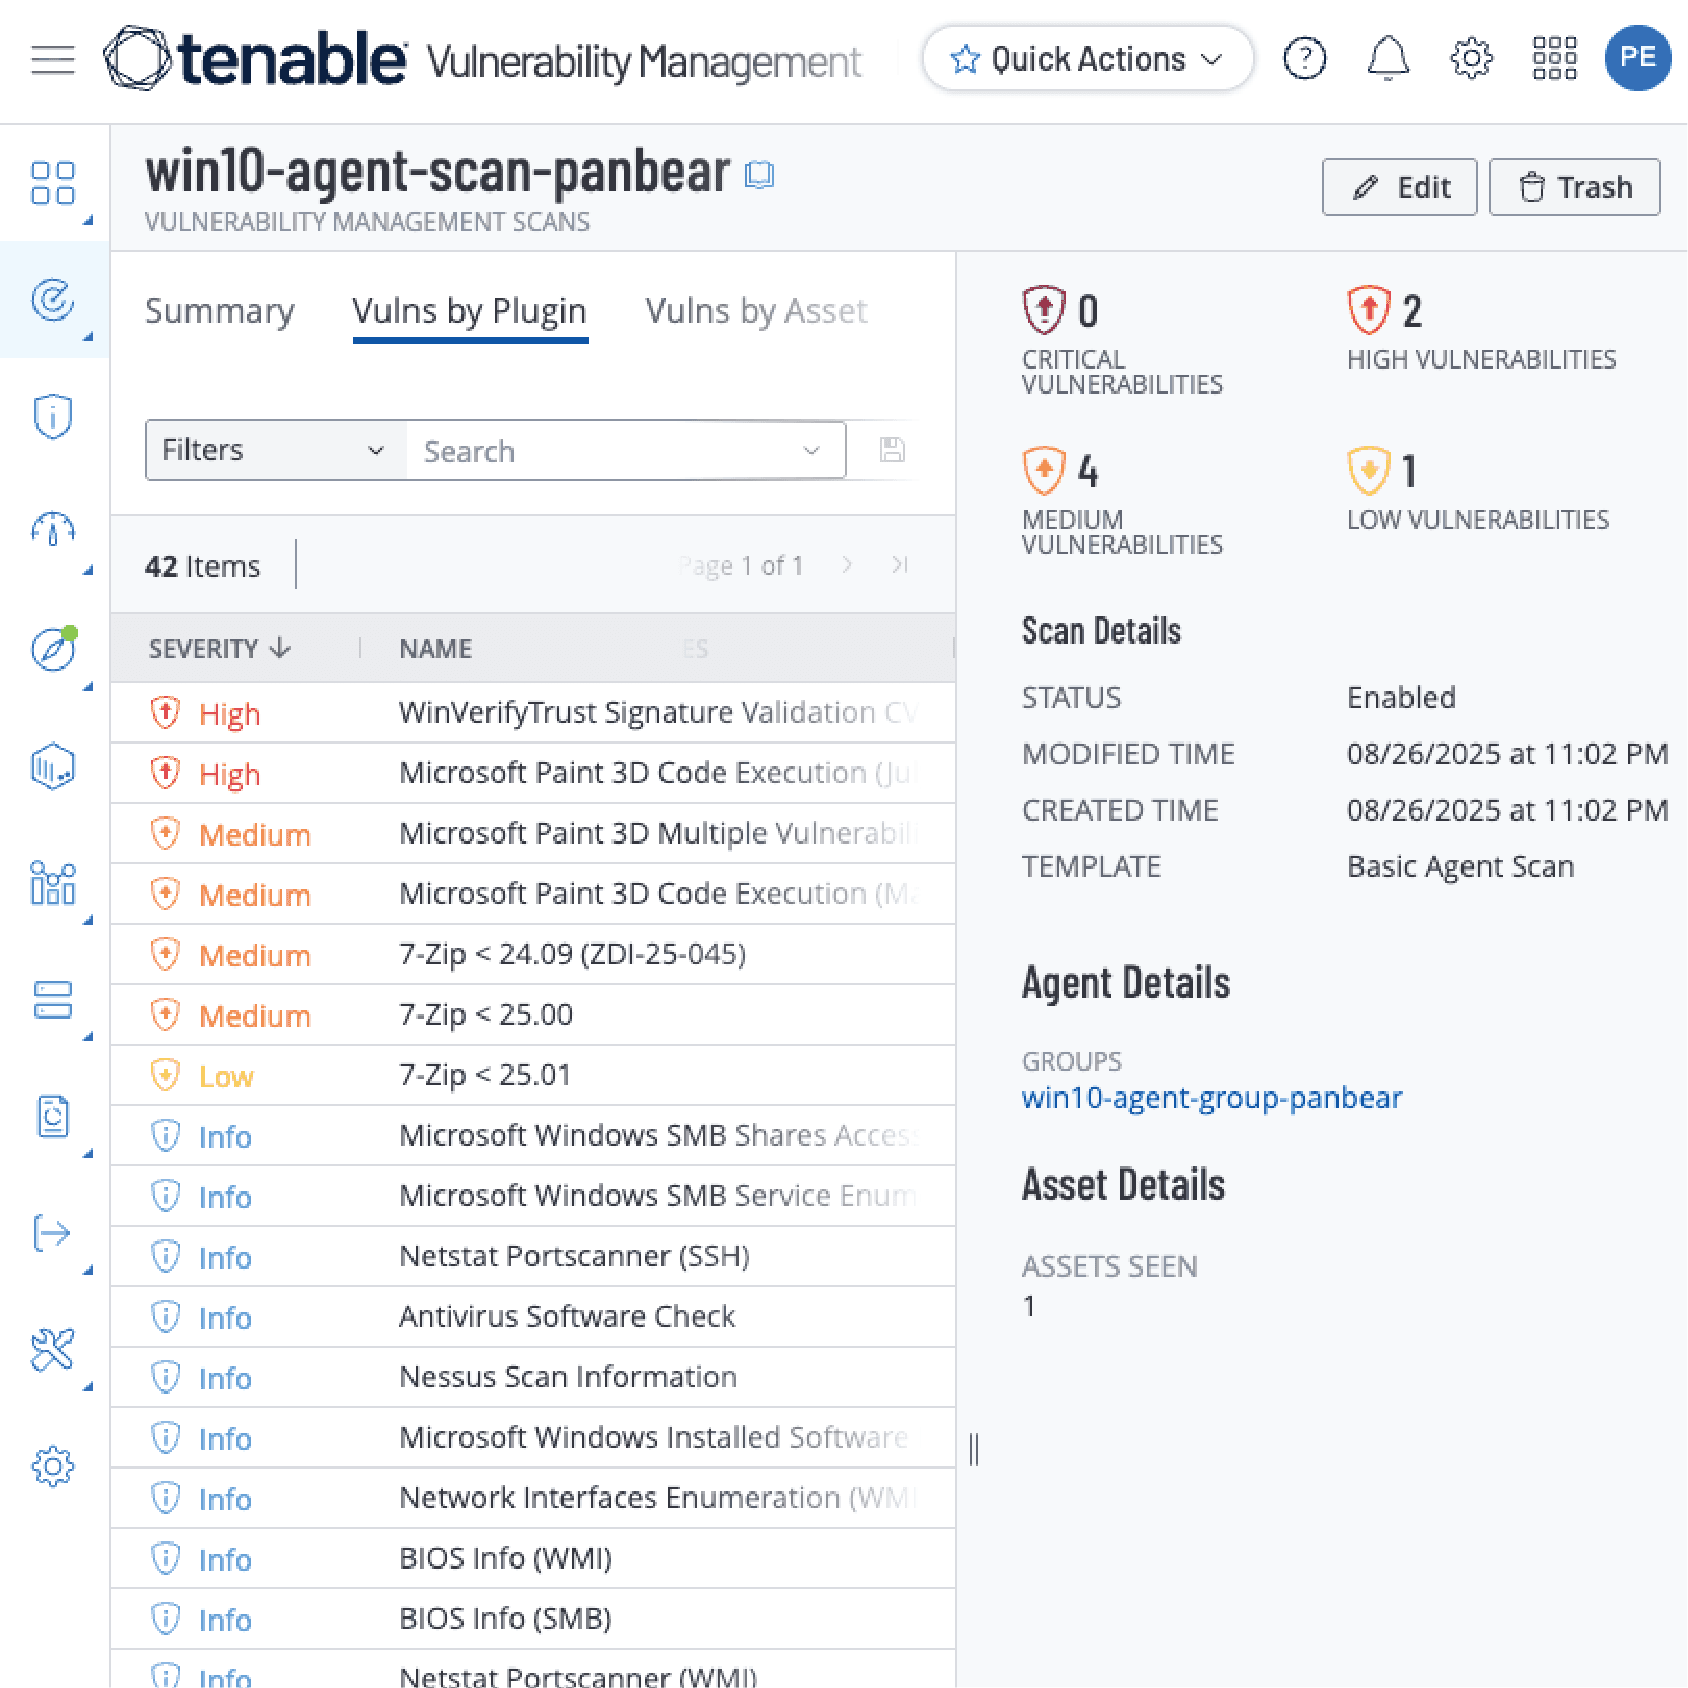
Tenable Vulnerability Management agent scan of a Windows 10 lab machine, findings listed by severity

04 / 04

04 · Tenable agent scan, Windows 10

04 · Tenable agent scan, Windows 10

ENLARGE

ENLARGE

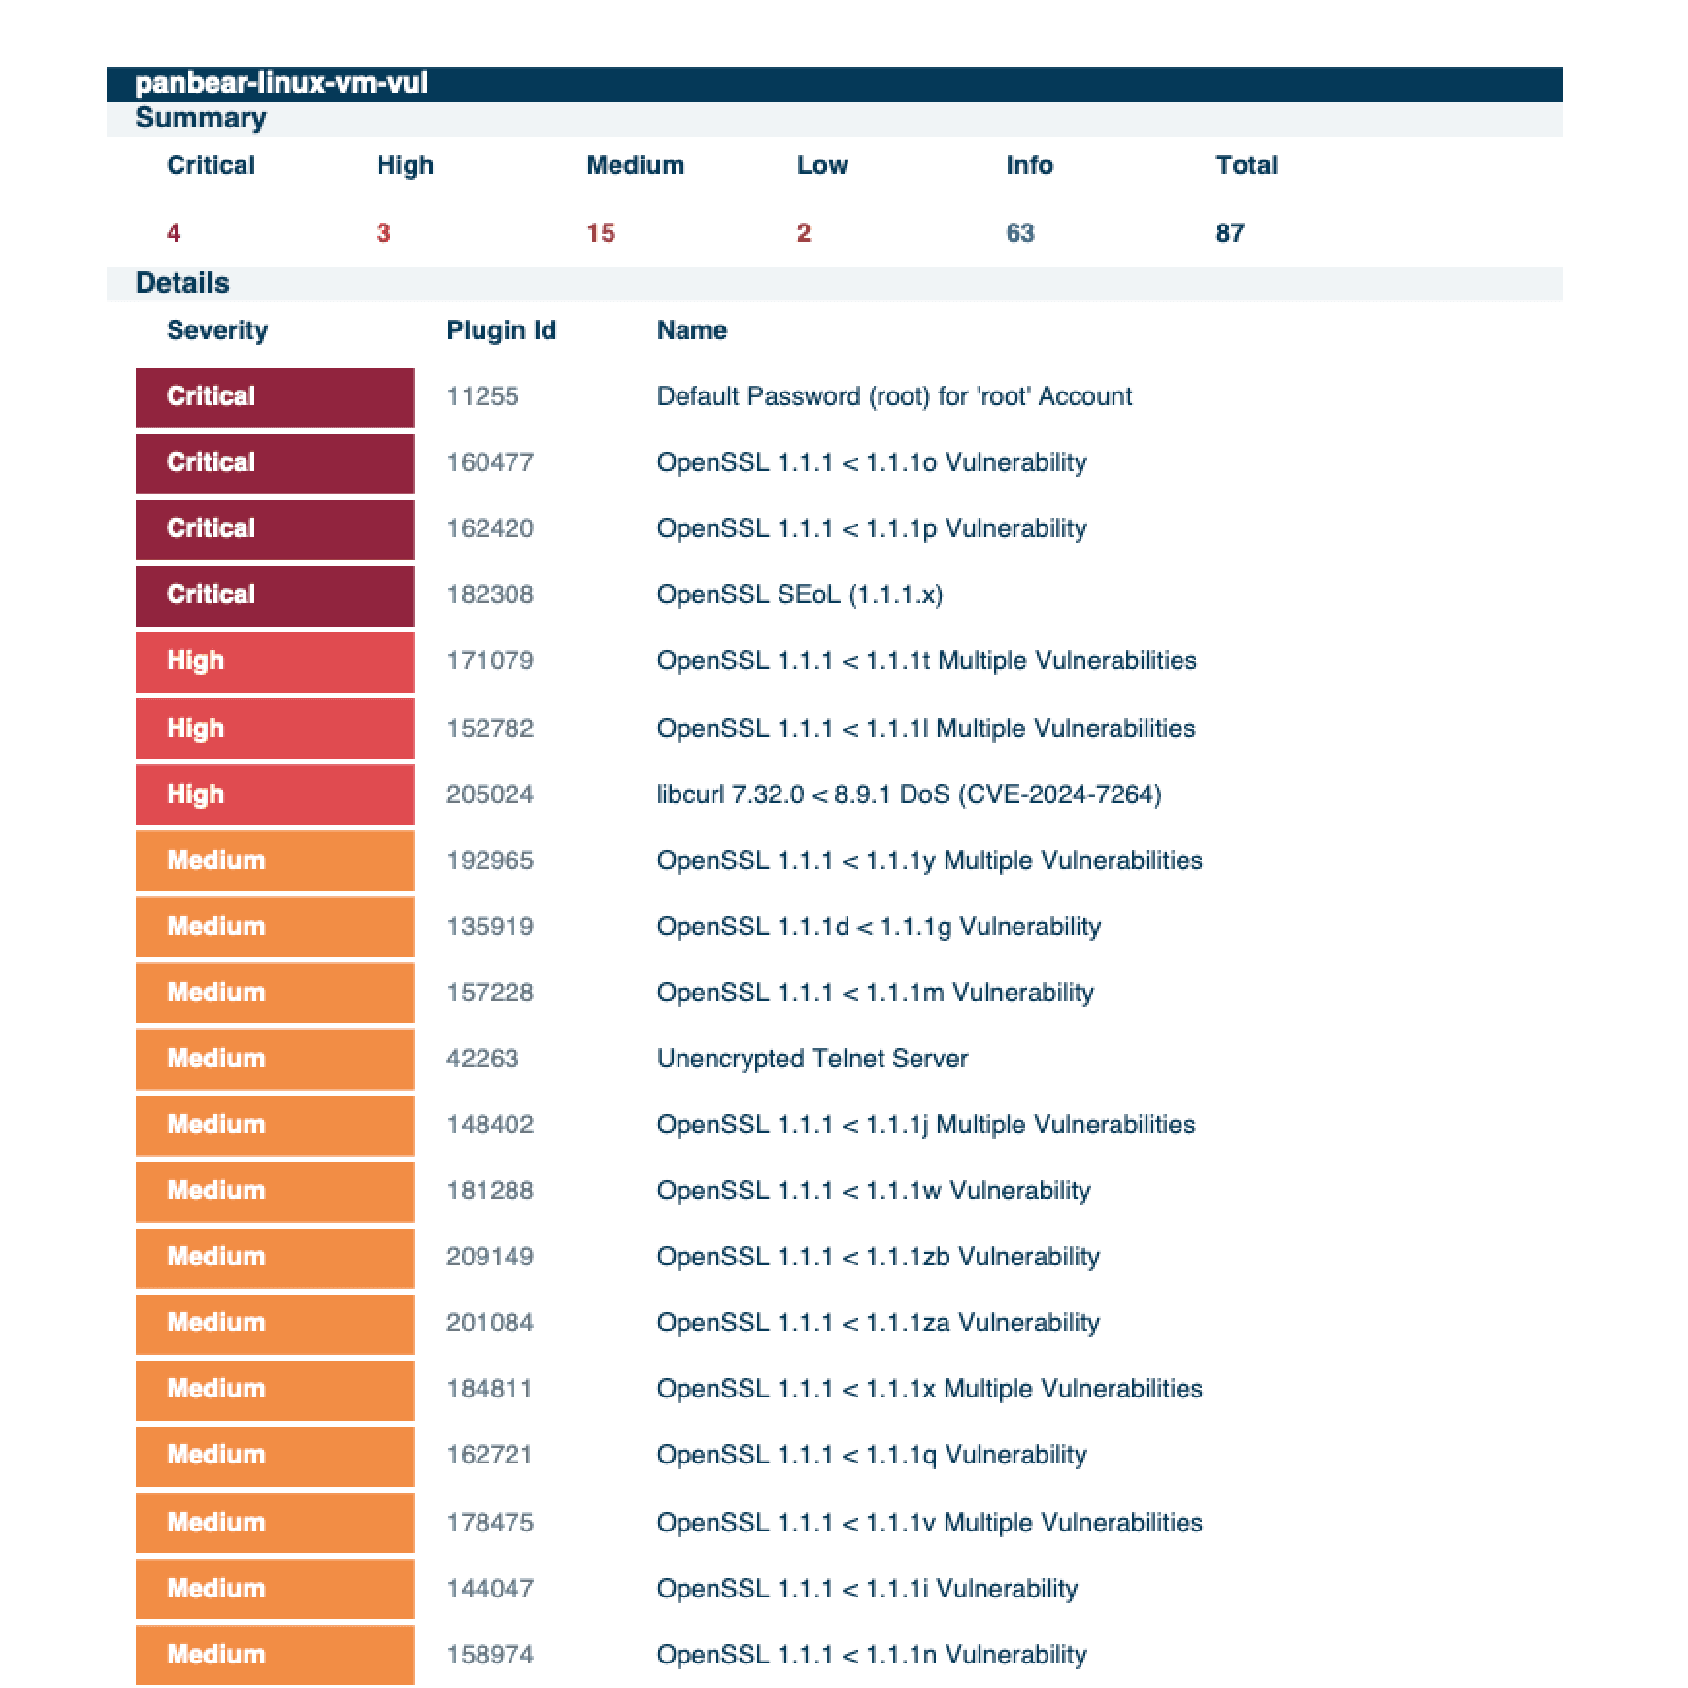
Vulnerability report for a Linux lab VM: 4 critical, 3 high, 15 medium findings, colour-coded by severity

05 · Scan report, vulnerable Linux VM

ENLARGE

Azure portal: network security group inbound rules for a lab VM, with the Add inbound security rule panel open

06 · Azure network security group rules

ENLARGE

04 / 04 · WEAK SPOTS

04 / 04 · WEAK SPOTS

Finding weak spots, closing doors

Finding weak spots, closing doors

Finding weak spots, closing doors

Hunting shows what already happened; scanning shows what could happen next. I ran a Tenable agent scan on a Windows 10 lab machine and a vulnerability scan on a Linux VM left weak on purpose, then worked through the findings by severity: a default root password, outdated OpenSSL, an unencrypted Telnet server. In Azure I edited network security group rules to control which ports each lab machine exposed.

Hunting shows what already happened; scanning shows what could happen next. I ran a Tenable agent scan on a Windows 10 lab machine and a vulnerability scan on a Linux VM left weak on purpose, then worked through the findings by severity: a default root password, outdated OpenSSL, an unencrypted Telnet server. In Azure I edited network security group rules to control which ports each lab machine exposed.

Hunting shows what already happened; scanning shows what could happen next. I ran a Tenable agent scan on a Windows 10 lab machine and a vulnerability scan on a Linux VM left weak on purpose, then worked through the findings by severity: a default root password, outdated OpenSSL, an unencrypted Telnet server. In Azure I edited network security group rules to control which ports each lab machine exposed.

LAB WORK

Vulnerability management lab ↗

Vulnerability management lab ↗

CONTACT

Let’s talk.

Let’s talk.

Let’s talk.

Open to security operations and safety roles, and always up for a good conversation about any of the six chapters.

Open to security operations and safety roles, and always up for a good conversation about any of the six chapters.

© 2026 PETER W. PAN · BEAR ON WATCH